| Detection rule authoring |
YARA, Sigma, MISP/IOC |
Manual / bespoke task |
| Threat hunting logic generation |
Built-in |
Manual / bespoke task |
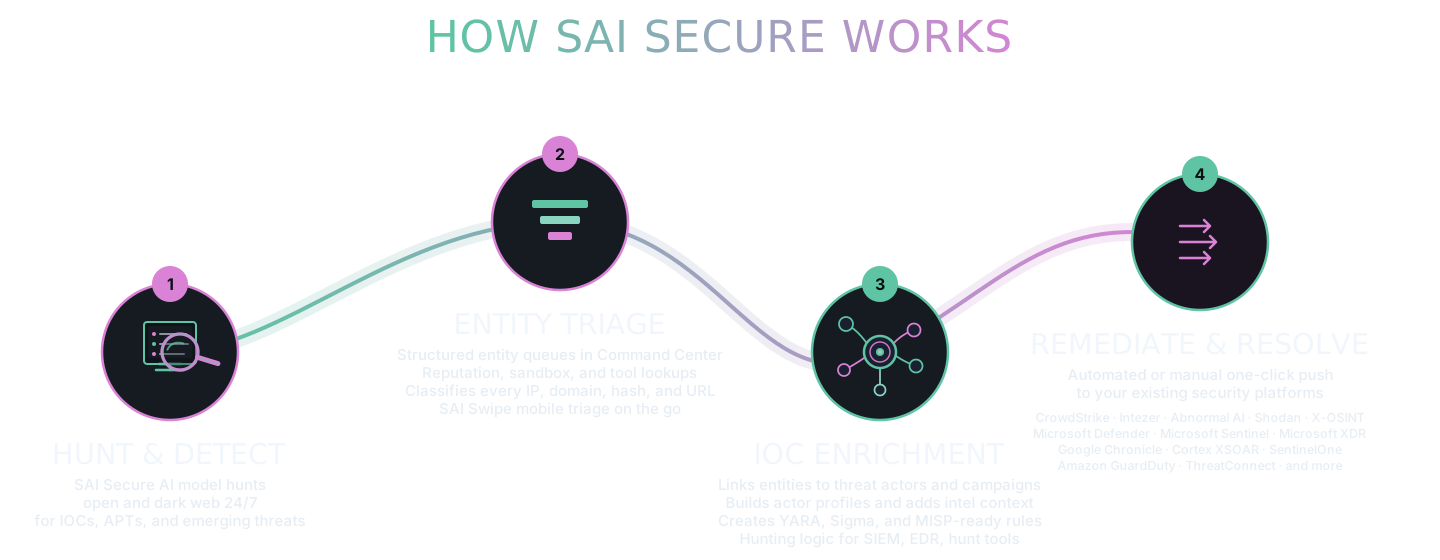
| Structured entity triage |
IP, hash, domain, process |
Generic enrichment |
| Multi-modal AI investigation agents |
Orchestrated |
Single-model / manual |
| Analysis guardrails & prompt engineering |
Built-in |
- |
| AI threat hunting agent & unified command workspace |
Core platform |
Not primary focus |
| Adversary + LM/TI & underground intelligence |
Curated feeds |
Core strength |
| Dark web clarity intelligence |
Query-driven |
Analyst-led feeds |
| Deep & dark web monitoring |
Query + enrichment |
Monitor-as-a-service |
| Entity triage queues & operational workflows |
Built-in |
Intelligence-led |
| Custom triage detectors |
User-defined linking |
- |
| Full API & SAI tools automation |
Programmatic access |
Limited / UI-only |
| True positive push to EDR / XDR |
EDR and security platforms |
Manual export |
| Mobile triage (SAI Swipe) |
Included |
- |
| Attack surface & third-party exposure |
Limited |
Exposure platform |
| Digital risk protection & takedowns |
- |
Included |
| Behavioral threat hunting |
AI-assisted |
Collect hunt packs |
| Knowledge base & analyst runbooks |
Built-in |
Finished intel reports |